Unique passwords prevent one leak becoming ten
Reusing a password means one breached website can put other accounts at risk. A trusted password manager can create and save long random passwords, so each service has its own secret. Protect the manager itself with strong authentication and safe recovery options.
Enable the strongest MFA available
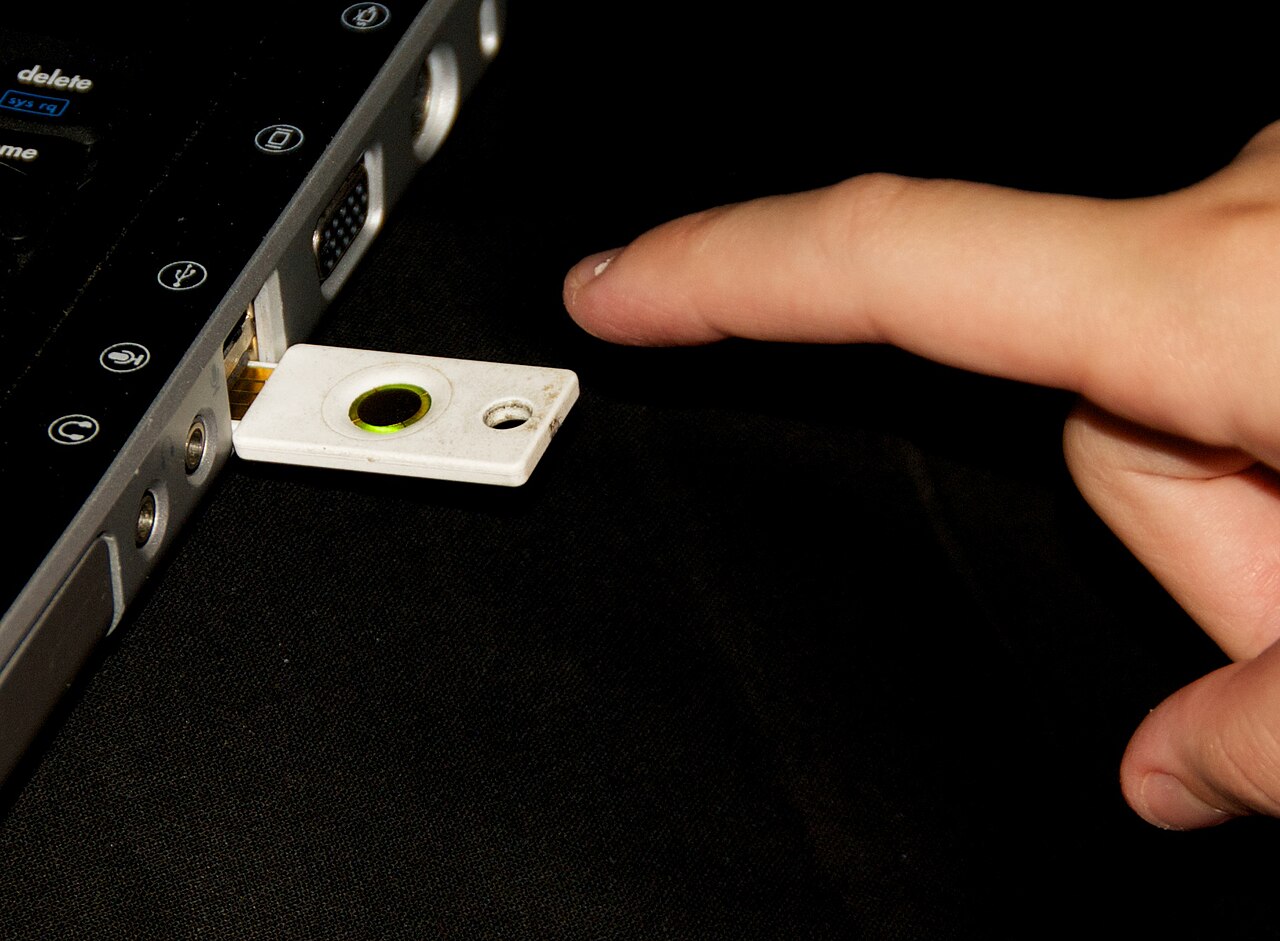
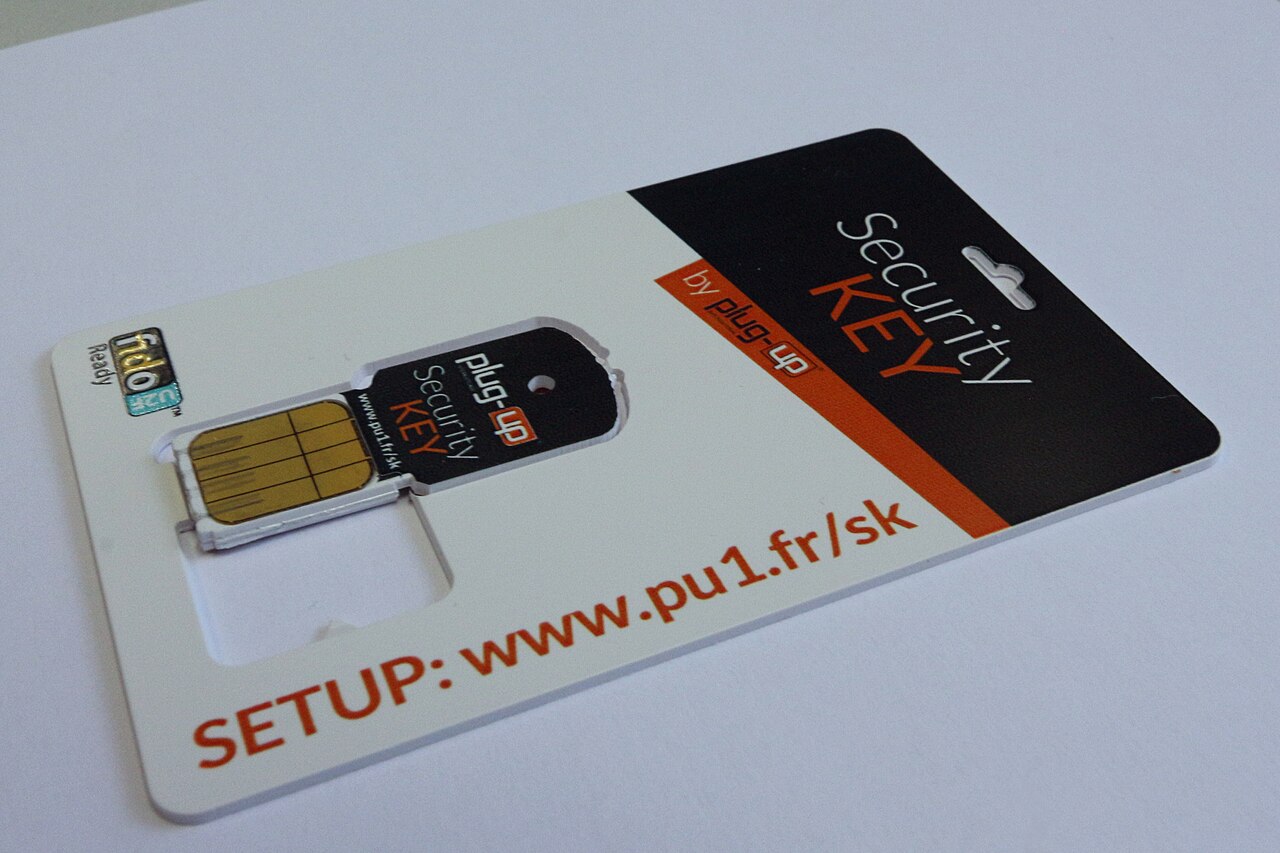
Multifactor authentication adds another check besides the password. Where offered, passkeys or security keys can resist phishing better than SMS codes. Save recovery codes offline and verify device replacements before discarding an old phone.
Install updates rather than postponing them
Operating-system, browser and app patches address known vulnerabilities. Enable automatic updates where practical, restart when necessary and avoid unofficial cracked installers. Retire unsupported devices if they can no longer receive essential security fixes.
Verify messages through a trusted route
Urgent messages that demand a login or card details may be phishing. Open a known official app or type the legitimate website yourself rather than following an unsolicited link. Report suspicious messages using the service's own controls.
A general educational overview, not a substitute for professional guidance. Check current local rules and trusted primary sources before making consequential decisions.
Share this article